NIST SHA-3 streaming-interface draft
From CDG’s Oct 21 company post: Released October 8, the initial public draft of SP 800-185 Revision 1 covers cSHAKE, KMAC, TupleHash and ParallelHash. It adds streaming interfaces for extendable-output…
Source: Cyber Defense Group. Original reporting and dates are preserved.
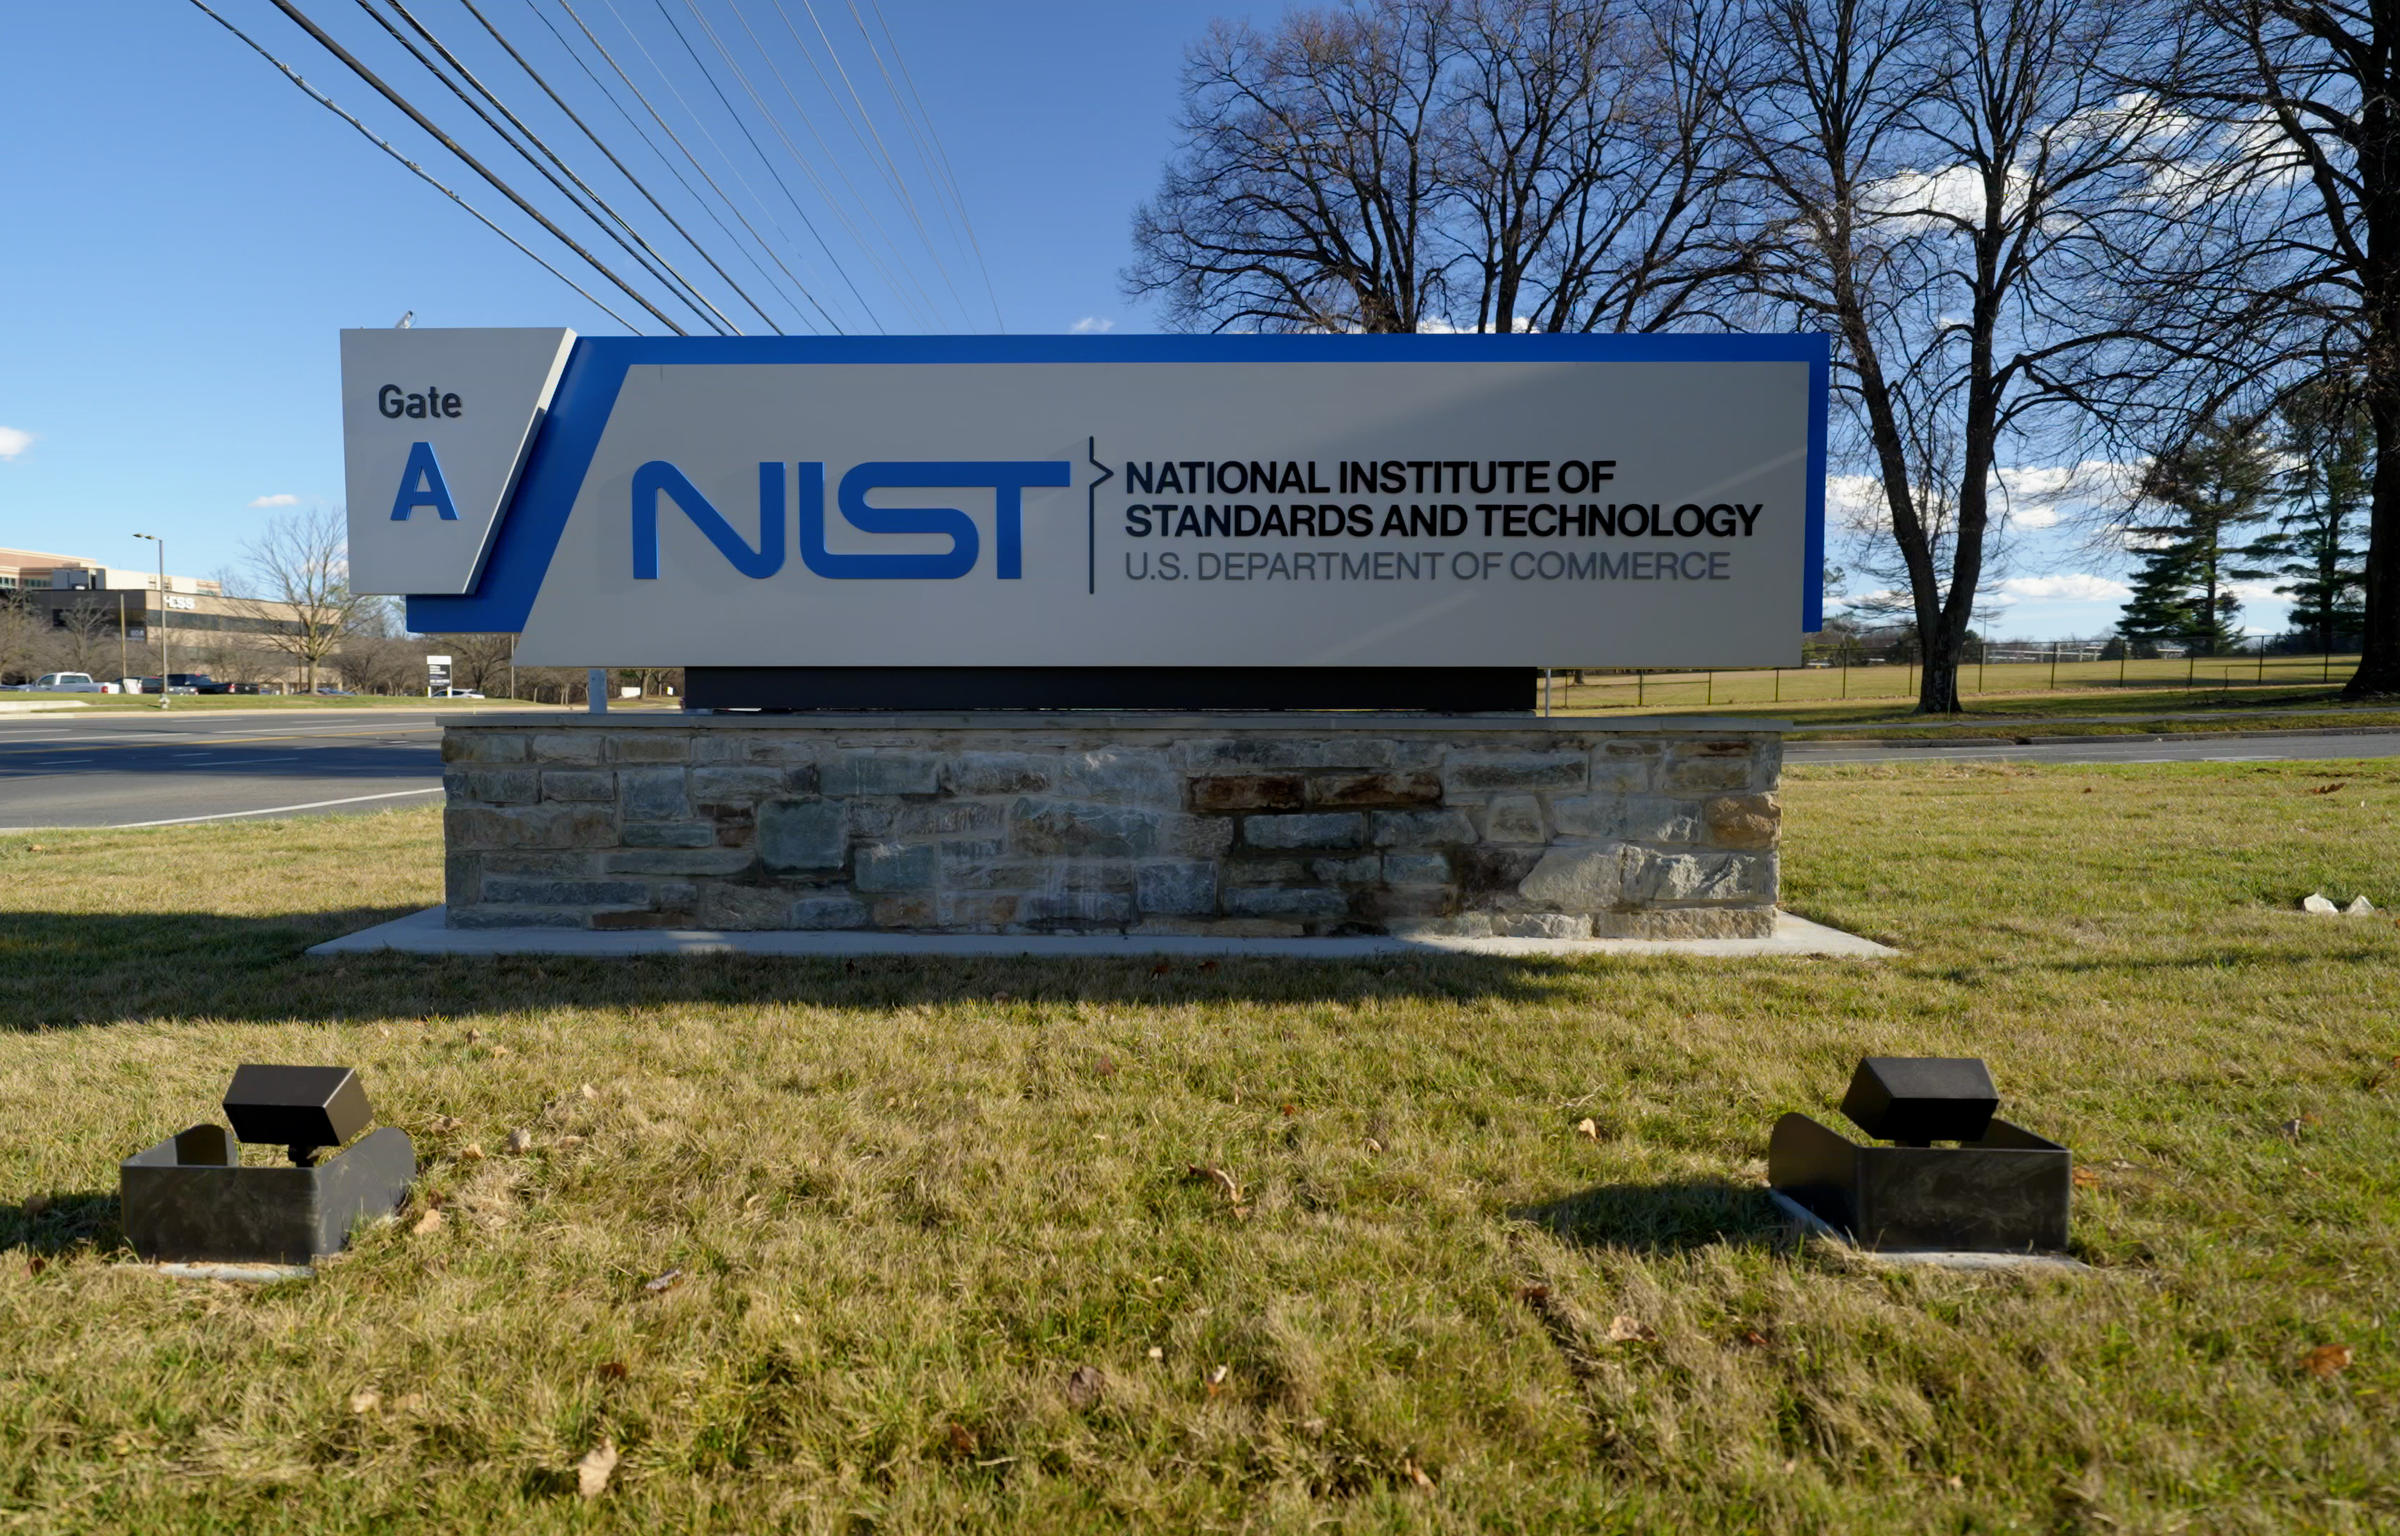
NIST Gaithersburg Gate A entrance sign, published January 2025. Agency context for historical draft-standard coverage; not a final-standard announcement. No endorsement implied.
R. Eskalis/NIST · NIST public information; reuse with credit · LicenseThe photograph above has its own source and credit. Image references in the original reporting below may describe a different image on the source publication.
Original CDG company post
NIST’s SHA-3 draft targets an implementation detail that matters: streaming data.
Released October 8, the initial public draft of SP 800-185 Revision 1 covers cSHAKE, KMAC, TupleHash and ParallelHash. It adds streaming interfaces for extendable-output function (XOF) computations, allowing applications to process input and request output incrementally without knowing the total lengths in advance.
The draft describes INIT, ABSORB and SQUEEZE operations. NIST says the single-call interfaces remain equivalent to the functions in the previous version, and specifically requests feedback on how TupleHash handles complete tuple elements.
For federal technology teams and suppliers using these functions, this is an opportunity to review library interfaces, implementation assumptions and test coverage before the revision is finalized.
Comments are due December 7, 2026. This is a draft open for public comment, not a final standard or a new migration deadline.
Read the official draft and reviewer notes: https://lnkd.in/eM88JYYQ
Photo: R. Eskalis/NIST, NIST Gaithersburg campus. Used for editorial coverage; no NIST endorsement implied.
#NIST #Cryptography #FederalIT #CyberDefenseGroup
Sources and references
Source publication notes
Historical technology archive. This original commentary does not describe CDG’s current consulting services and is not current security or compliance guidance.
Preserved from CDG’s company LinkedIn history. Original publication dates are retained; later updates may change the source, status, or deadlines.
The original CDG graphic is reproduced above. See its image credit, source and reuse terms.
Educational information, not legal advice. Current official program guidance and the instructions for your application control. Registration, certification, or consulting does not guarantee an award.